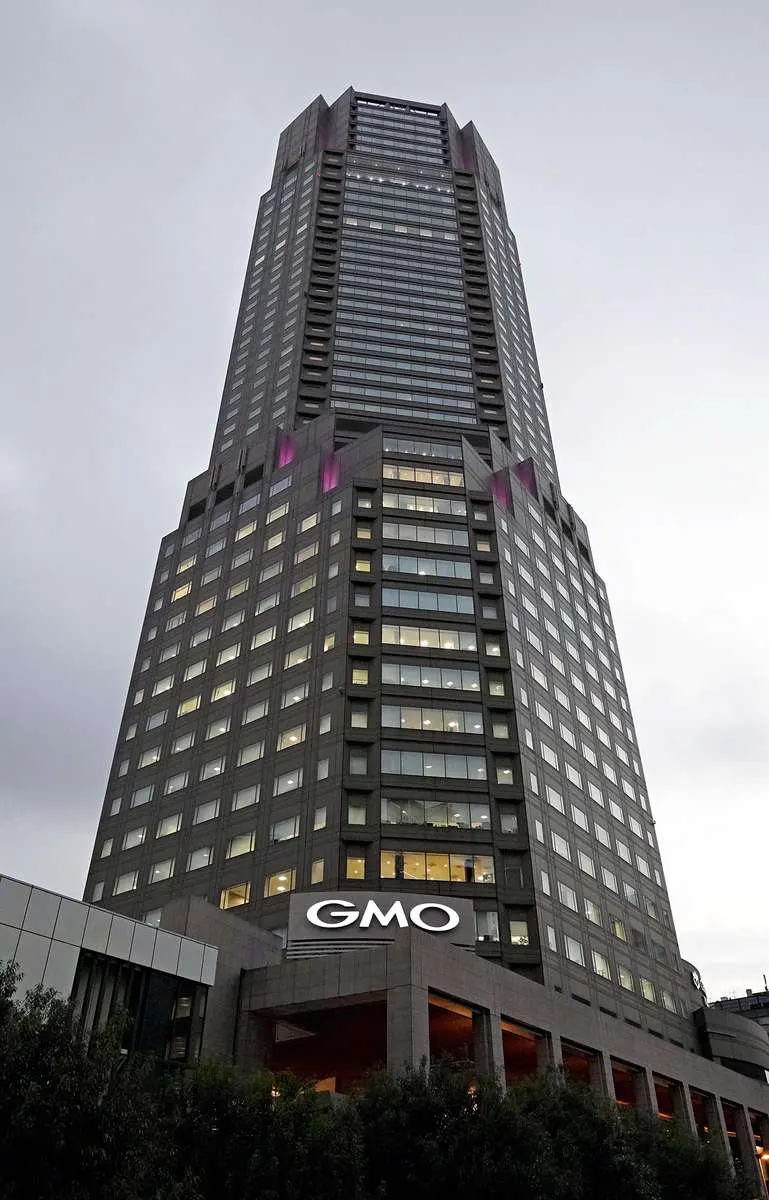
- GMO Internet Group, Inc. announced on Friday, November 13, 2026, that it expects to incur approximately ¥3.05 billion in direct expenses to compensate users who suffered financial losses due to an unauthorized access incident.
- The security breach targeted the “Onamae.com Desktop Cloud” service—a cloud environment used for margin trading in the foreign exchange (FX) market operated by a GMO subsidiary.
- As of reporting figures disclosed during an investor earnings briefing, claims totaling ¥2.99 billion have been filed across 2,943 user accounts following illicit manipulation and unauthorized trades.
- In addition to full loss compensation, GMO confirmed that it is processing flat ¥5,000 sympathy payments to eligible users, with 10,976 applications received out of 26,739 eligible cases as of Thursday, November 12.
- Executive leadership, including the CEO, previously accepted monthly pay cuts ranging from 20% to 25%, while the corporation plans to book all related financial impacts within the October–December 2026 quarter.
Japan (Japan Daily News) November 14, 2026 – GMO Internet Group, Inc. announced on Friday, November 13, 2026, that it anticipates incurring approximately ¥3.05 billion in costs to fully compensate users impacted by a cyberattack on its FX trading cloud infrastructure. Disclosing the figures during an investor earnings briefing, executives revealed that claims covering 2,943 accounts total roughly ¥2.99 billion. The security breach, which came to light in late October, involved unauthorized third-party access to login credentials on the Onamae.com Desktop Cloud service, leading to fraudulent transactions. GMO confirmed it will book the expenses in the fourth quarter while continuing to process separate ¥5,000 consolation payments for affected customers.
- What Are the Specific Financial and Operational Figures Associated With the GMO Breach?
- How Do the Components of GMO’s Customer Restitution Package Compare?
- Background of the Particular Development After the News
- How This Development Can Affect Retail FX Traders, Cloud Providers, and Corporate Governance
As reported by financial and corporate news desks, GMO Internet Group, Inc. formally outlined the financial fallout of the late-October security breach during its quarterly earnings briefing on Friday, November 13, 2026. The incident stemmed from unauthorized third-party access to the servers powering the Onamae.com Desktop Cloud service, a virtual private server environment heavily utilized by traders to run foreign exchange margin trading platforms such as MetaTrader.
According to corporate disclosures, intruders exploited system vulnerabilities to harvest user login credentials and passwords. This credential exposure enabled malicious actors to execute unauthorized trades within client accounts, resulting in substantial financial losses for numerous retail traders.
Addressing shareholders and analysts, corporate representatives stated that the company will record total expenses of approximately ¥3.05 billion during the October–December 2026 quarter to cover full customer restitution. Of that total, claims specifically tied to fraudulent FX transactions account for 2,943 user accounts, amounting to ¥2.99 billion. Furthermore, GMO confirmed that it is distributing a flat ¥5,000 goodwill sympathy payment to acknowledge customer anxiety and service disruption; out of 26,739 eligible user accounts, 10,976 applications had been formally received as of Thursday, November 12.
Company executives emphasized that GMO is committing to full reimbursement of realized trading losses, going beyond strict liability terms. Concurrently, senior management accepted direct accountability, with executive leadership implementing voluntary monthly salary reductions. While cyber insurance policies are anticipated to offset a portion of the payout, the firm confirmed that its overarching financial forecasts and dividend projections remain temporarily under review as comprehensive cybersecurity overhauls are finalized.
What Are the Specific Financial and Operational Figures Associated With the GMO Breach?
Corporate disclosures and financial reports released on November 13, 2026, outline the core metrics of the incident:
- Total Expected Financial Impact: Approximately ¥3.05 billion to be booked in the fourth quarter (October–December 2026).
- Formal Loss Claims: ¥2.99 billion submitted across 2,943 user accounts experiencing unauthorized trading activity.
- Consolation Payments: A flat ¥5,000 goodwill payment offered to eligible users, drawing 10,976 applications out of 26,739 qualifying accounts as of November 12.
- Affected Platform: Onamae.com Desktop Cloud, operated by a subsidiary of GMO Internet, Inc.
- Management Accountability: Executive leadership implemented voluntary monthly pay reductions ranging from 20% to 25%.
How Do the Components of GMO’s Customer Restitution Package Compare?
A structured breakdown illustrates how GMO Internet Group structured its financial response to affected platform users:
| Restitution Component | Target Scope & Eligibility | Financial Value / Scale | Purpose & Implementation |
| Unauthorized Trade Loss Compensation | Users who suffered confirmed realized trading losses, fees, and charges from malicious account manipulation. | ¥2.99 billion across 2,943 reported accounts. | Full reimbursement of direct financial harm caused by third-party access without applying strict service-agreement caps. |
| Flat Consolation (Sympathy) Payment | All active users registered on the Onamae.com Desktop Cloud service during the incident window (26,739 eligible cases). | ¥5,000 per user (10,976 applications received by Nov 12). | Goodwill gesture acknowledging operational inconvenience and anxiety, independent of direct trading losses. |
Background of the Particular Development After the News
The security breach affecting GMO Internet Group’s Onamae.com Desktop Cloud service emerged in late October 2026, quickly escalating into a high-profile corporate crisis. Cloud-based virtual private servers (VPS) are widely employed by retail foreign exchange traders in Japan to maintain continuous automated trading strategies via platforms like MetaTrader 4 and 5. The compromise of shared administrative infrastructure allowed unauthorized parties to harvest stored credentials, execute fraudulent transactions, and briefly expose sensitive data.
In response to the incident, Japanese authorities and corporate governance bodies scrutinized digital risk management across cloud providers. GMO rejected external extortion demands following a ransom threat, opting instead to establish a cybercrime bounty program, overhaul its security architecture using advanced verification frameworks, and commit to absolute customer restitution to preserve institutional trust.
How This Development Can Affect Retail FX Traders, Cloud Providers, and Corporate Governance
The allocation of ¥3.05 billion in compensation and ongoing security overhauls by GMO Internet Group are projected to influence key stakeholders across Japan’s digital and financial sectors:
1. Heightened Security Standards and Client Migration for Cloud and VPS Providers
For Japanese cloud service providers and hosting operators, the incident serves as a regulatory and operational warning, accelerating the adoption of multi-factor authentication, segregated administrative controls, and robust credential encryption to prevent credential-stuffing vulnerabilities.
2. Restored Consumer Confidence and Transparent Recourse for Retail FX Traders
For individual foreign exchange traders utilizing virtual desktop environments, GMO’s commitment to full loss reimbursement and goodwill compensation establishes a vital precedent for corporate accountability following third-party cloud compromises.
3. Stricter Risk Management and Board-Level Oversight for Listed Technology Firms
For corporate boards across Japan’s technology sector, the financial penalty and executive pay reductions underscore the immediate connection between cybersecurity preparedness, executive liability, and investor relations.